X069-BELGICA HACKER EXPLICACION NEVERAS
Hackers who cranked up fridge temperatures in dozens of store across at least eight European nations on Monday (November 2) likely exploited a simple weakness: default passwords on open systems that were easy to guess, a cyber security expert told Reuters on Wednesday (November 4).
The second cyberattack in three weeks targeted fridge systems at supermarket chains including Carrefour and Delhaize in Belgium, and ICA and Coop in Sweden, and has put a spotlight vulnerabilities at reatailers that could threaten food security. Three blood banks in France were also hit.
Laurens Singier, an ethical hacker and researcher at Cyber 4 Lab, part of Howest University of Applied Science in Bruges, Belgium, walked Reuters through the weak spots of systems often accessible online and with thin protections.
"In this case, the weak point was mainly putting those devices on the public internet. They shouldn't even be there", he said, surround by servers and systems designed to replicate those that could control supermarket store fridges.
He added AI was also now making such hacks much easier for amateurs to pull off.
After the Monday hack, supermarkets on Tuesday said they had taken hacked fridges offline, in line with guidance from refrigeration monitoring software provider Danfoss, whose systems were again among those targeted.
Danfoss has said it is working with clients on fixes.
DESCRIPCIÓN DE IMÁGENES
Here's how hackers got inside Europe's supermarket fridges
VIDEO SHOWS: ETHICAL HACKER INTERVIEW ON FRIDGE HACKING INCIDENTS, SHOWING HOW IT CAN BE DONE
SHOWS: BRUGES, BELGIUM (NOVEMBER 4, 2026) (REUTERS- Access all)
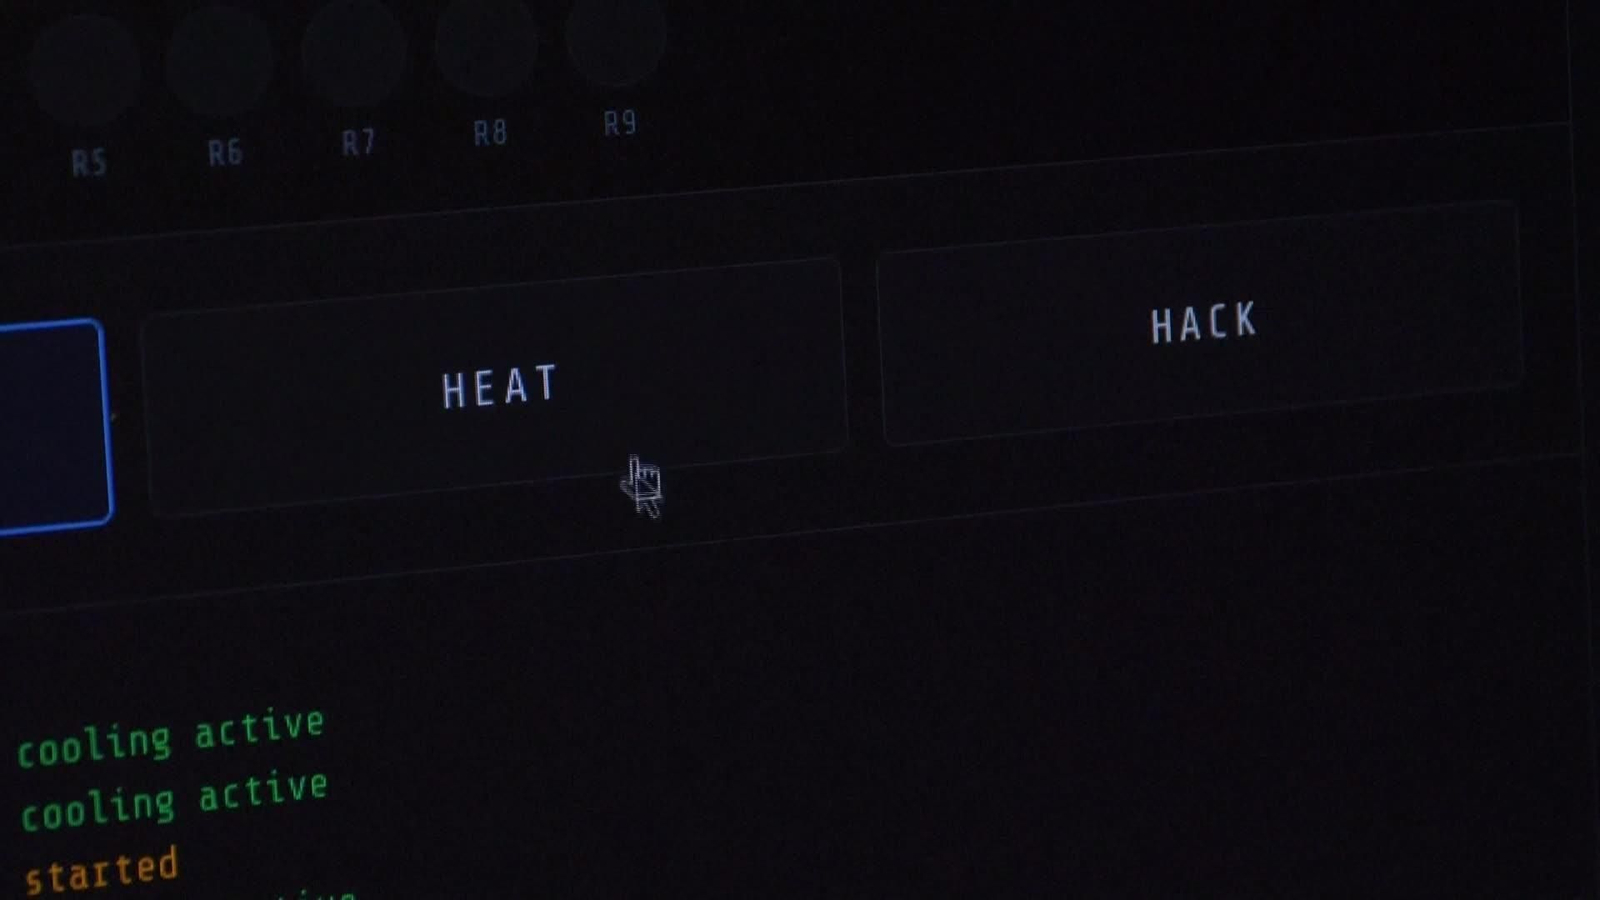
1. VARIOUS OF COMPUTER SCREEN SHOWING INTERFACE DEMONSTRATING HACKING OF REFRIGERATION SYSTEM
2. HANDS TYPING ON KEYBOARD
3. MOUSE MOVING TO BUTTON READING 'HACK'
4. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"It's a website, just like facebook.com or anything that is hosted on a PLC, a programable logic controller, one of these cases which basically controls refrigeration units. So in a store we might have like 100 freezers, we don't want to individually control all those freezers, so we put a computer in front of it who makes sure that the heating and cooling turns on the correct times and we need to control that computer, so there's a web interface to do that. The biggest flaw here was putting that weapon for face public so anyone can control it and the second mistake they make is using default credentials on most of these."
5. SCREEN SHOWING USERNAME AND PASSWORD 'ADMIN'
6. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"So I try to log in, Admin 12345 and I'm seeing the interface to cool system. If I press the button, heating will turn on. If I press the other button hitting will turn off again, and also made a hack mode where it shows the system is being manipulated."
7. LIGHTS BLINKING REPRESENTING REFRIGERATOR SYSTEM BEING HACKED
8. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"During the night, attackers gained control over publicly-exposed interfaces kind of like websites like we visited Facebook where they could just simply log in by the default credentials: Admin, Admin, Admin 1234, and gain access to basically the system, to control the heating and cooling of those systems, making sure at one press of the button, would make it so they go into 'defrost' modes and a lot of foods became waste."
9. LIGHTS BLINKING REPRESENTING REFRIGERATOR SYSTEM BEING HACKED
10. HACKTIVIST GROUP ANONYMOUS MASK / MACHINE SIMULATING REFRIGERATOR SYSTEM BEING HACKED
11. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"Anything on the public internet can be found by anyone So it's really easy to find it anywhere in the world. There is some idea of location, so they could target specifically France, specifically Belgium; but to say specifically Delhaize or specifically Albert Heijn, it's actually quite hard because you don't really know what device is behind it or which, or who is the owner of the device. So I think that that was more of a general sense targeting a specific country or specific region and it was just that contractor who used those vulnerabilities and that's why he was hit on such a large scale."
12. SWEATER READING "HOWEST SECURITY"
13. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"In this case, the weak point was mainly putting those devices on the public internet. They shouldn't even be there. The second mistake they made is not changing the default passwords. And the third mistake was there was still quite a lot of older versions of those systems who had a known exploit out there that, could make it so that passwords can be guessed even though it was changed in the past."
14. VARIOUS OF MAP ON SCREEN SHOWING INDUSTRIAL DEVICES CURRENTLY PUBLIC ON INTERNET
15. HANDS TYPING
16. CODE
17. (SOUNDBITE) (English) ETHICAL HACKER AND RESEARCHER AT CYBER 3 LAB, LAURENS SINGIER, SAYING:
"Attacks on industrial infrastructure are quite rare, and the target in this case is also quite unique, but I think it will be more a more common and prevalent thanks to AI, because one simple prompts can already generate like IDs and code to do these type of attacks."
18. VARIOUS OF MACHINE PARTS WHILE HACKING IS IN PROGRESS
19. DATA ROOM
20. EXTERIOR OF UNIVERSITY